
corporate IT security
ISO 27001 certification for professional firms: protecting data and enhancing the firm
ISO/IEC 27001 certification for law, notary, and accounting firms: how to adapt IT infrastructure, comply with NIS2, and enhance firm security with Lanpartners in Milan.
Deepfakes and digital evidence: how AI is changing evidence management and litigation
Generative artificial intelligence has made it easy to create fake but extremely credible videos, audio, and documents. Although deepfakes do not yet represent a mass case in Italian courtrooms, the conditions for their systemic impact on litigation are already all there: on the one hand, computer reproductions can be challenged as manipulated; on the other hand, [...]
Business continuity and backup: protecting the firm's business from data loss
For a law or notary firm, backup alone is not enough: while the former saves data, business continuity ensures that operations can continue even after a major failure or a ransomware attack. In this guide, we analyze the 3-2-1 backup rule (three copies, two different media, one offsite and immutable copy), the [...]
Incident Response for professional firms: what to do in the first 24 hours after a cyber attack
In this operational guide, we analyze in detail the response and management protocol for a data breach within law and notary firms, accounting practices, and tax consulting structures. The in-depth analysis examines the evolution of the cyber threat landscape and the specific vulnerability of professional firms, providing a technical timeline broken down for the first twenty-four hours […]

IT Concierge: the people-driven partnership that turns technology into value
In an increasingly digitized legal world, technology must not be a burden, but the silent engine that allows professionals to focus on their clients. Our IT Concierge service was created with this goal: we are not simple assistance providers, but strategic partners who take care of people's needs, anticipating […]
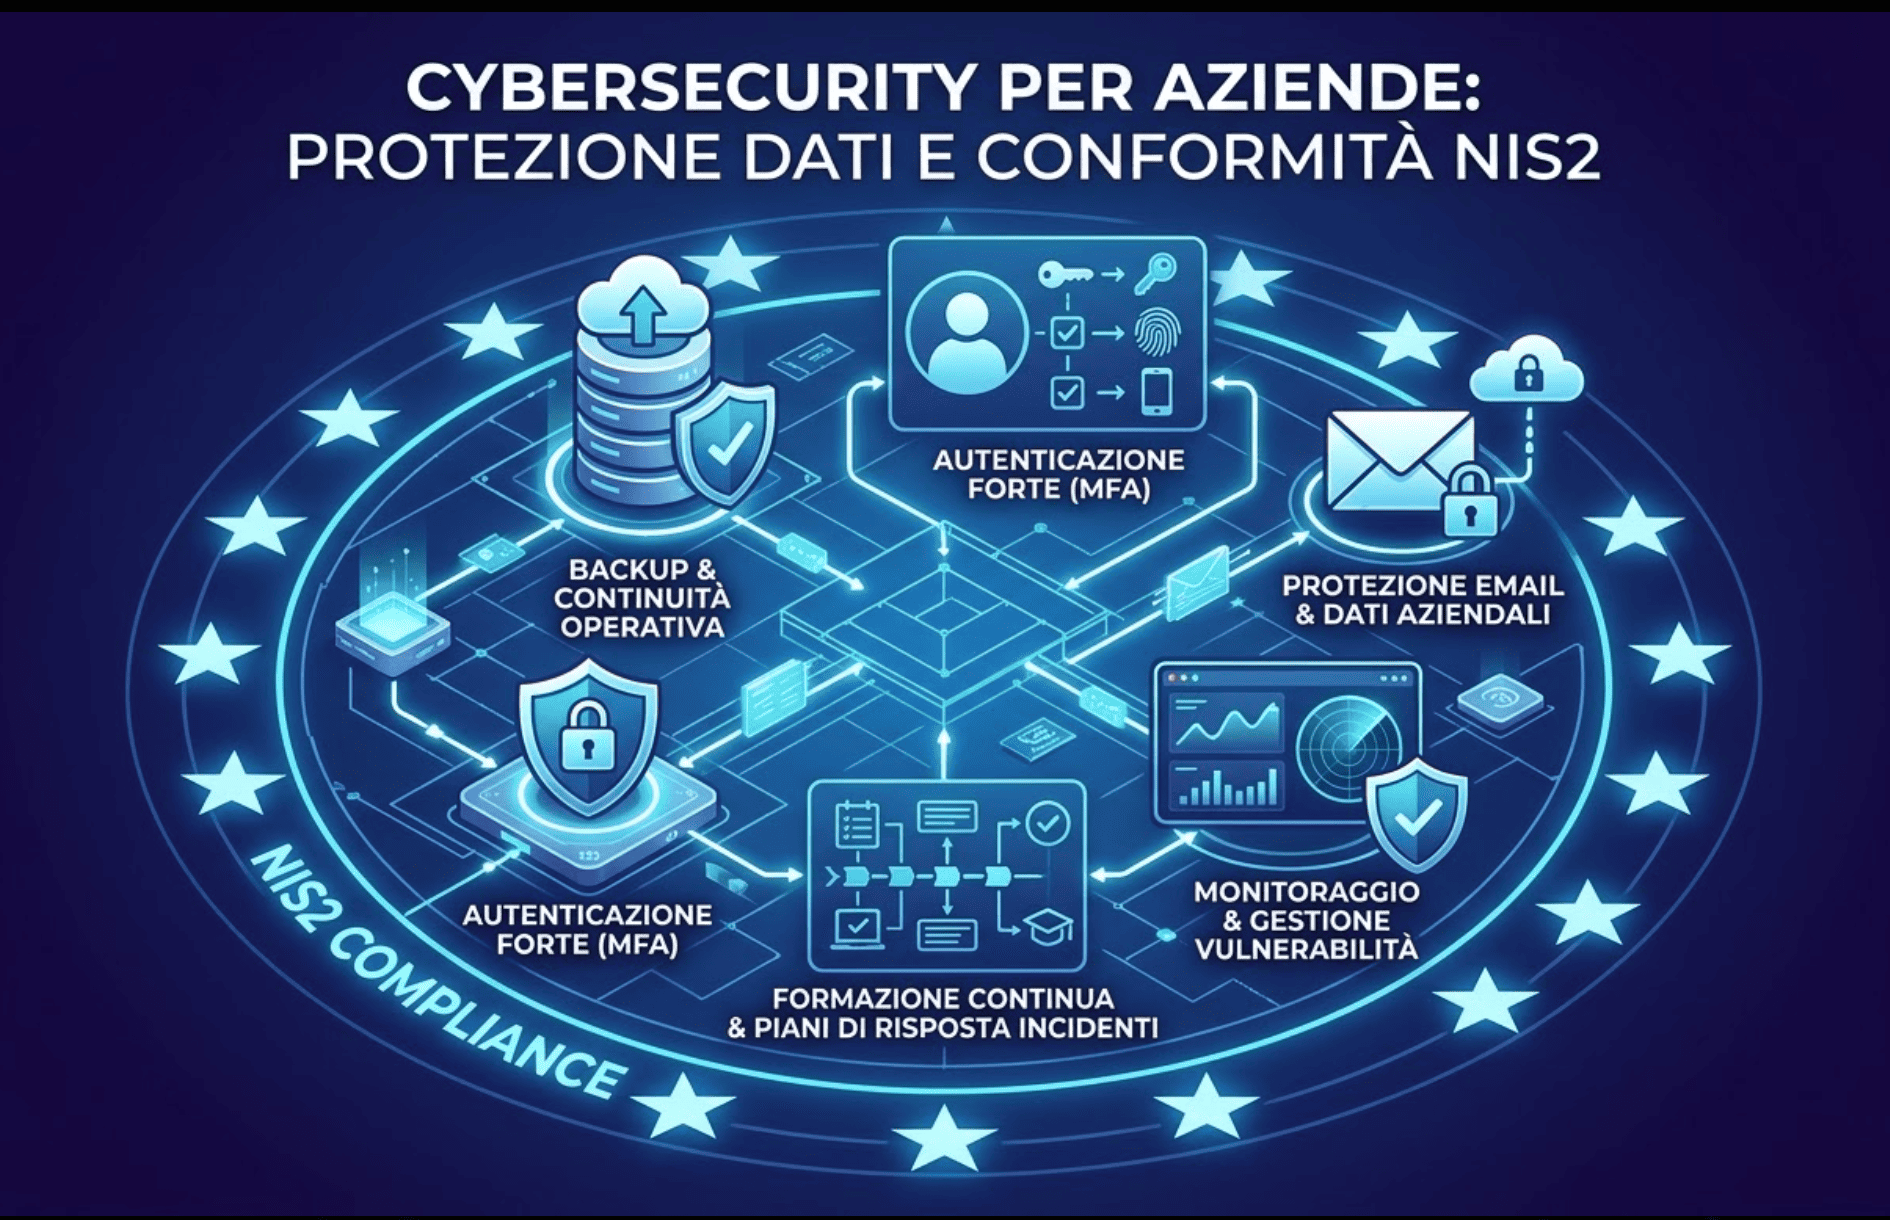
Cybersecurity for Businesses: Data Protection and NIS2 Compliance
This article is intended for businesses – particularly SMEs and organizations operating in regulated sectors – that want to understand concretely how to structure corporate cybersecurity and prepare for NIS2 compliance without hindering business operations. We will start with the real problem of increased attacks and sanctions, examine what changes with NIS2, and build a business [...]
Data Act 2025 and businesses: what changes for data sharing
Data Act in brief: the framework that will be fully operational in 2026. The Data Act is the European regulation on fair access to data and its use, designed to increase data availability in the EU, reduce vendor lock-in, and simplify data sharing between users, businesses, and public administrations. It entered into force on January 11th […]

disaster recovery and business continuity
Drawing up a disaster recovery and business continuity plan becomes essential for any SME that wants to protect data and operations in case of hacker attacks or malfunctions

SME digital security: key strategies 2025
Digital security strategies for SMEs in 2025: how to defend against advanced cyber threats and protect business
AI for law firms: identity theft prevention
Protect your business from the risk of identity theft by following simple best practices: here's how to do it
