
Cybersecurity for Businesses: Data Protection and NIS2 Compliance
Summary
TLDR
- The NIS2 Directive extends formal security obligations to many more companies and requires moving from a reactive approach to structured cyber risk management.
- NIS2 requires risk governance, documented policies, patching, strong authentication, encryption, network segmentation, tested business continuity, event monitoring, incident response, and staff training.
- The business case is built by estimating downtime days, daily revenue, recovery costs, penalties, and reputational damage, to be compared with a three-year security plan.
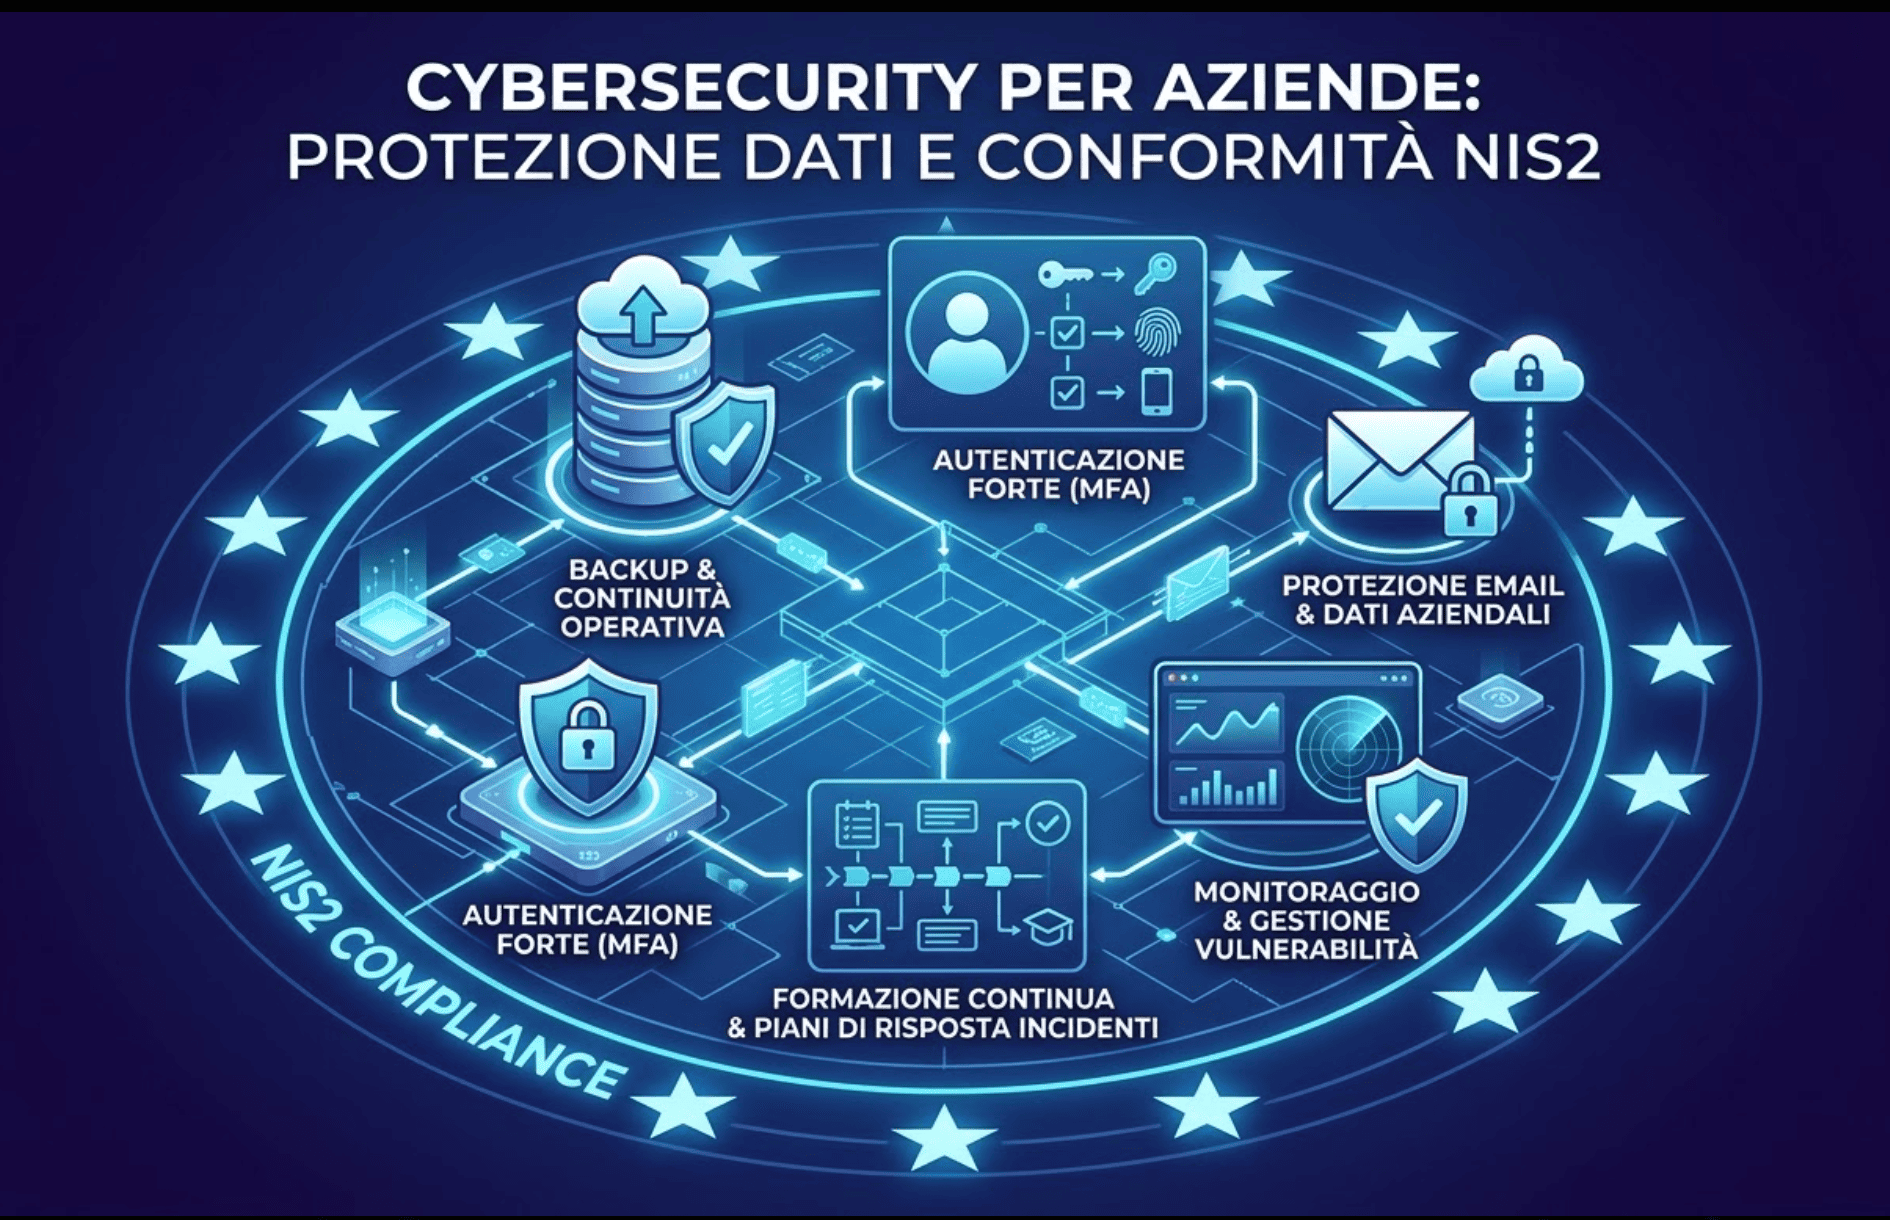
- The five minimum controls are backups with restoration tests, MFA, email protection, monitoring with vulnerability management, and training with incident response plans.
- Priorities vary by size: small companies start with the essential basics, medium ones with policies and centralized logs, and large ones with periodic audits and supply chain management.
Index
This article is designed for companies – particularly SMEs and entities operating in regulated sectors – that want to concretely understand how to structure corporate cybersecurity and prepare for NIS2 compliance without hindering business. We will start from the real problem of the increase in attacks and sanctions, see what changes with NIS2, build a simple business case on the costs and benefits of data protection, and distinguish priorities for small, medium, and more structured companies. We will delve into five “non-negotiable” security controls (backup, MFA, email security, monitoring, training) and conclude with the role of IT partners, like Lanpartners, in transforming compliance into a competitive advantage.
Why it makes sense to talk about cybersecurity and NIS2 today
In recent years, the ransomware attacks, data theft, and targeted phishing campaigns have increasingly affected SMEs as well, causing operational disruptions, ransom demands, and reputational damage that is difficult to recover from. The growing digitalization of processes, also described in the path of Digital transformation in SMEs , has made infrastructure, applications, and data central to business continuity.
The type of attacks affecting businesses has become more targeted: attackers gather information about the victim, study their digital dependencies, and exploit specific vulnerabilities to maximize impact. In many cases, the goal is not just to block systems, but to steal sensitive data and then use it as leverage, threatening to publish confidential information about clients, suppliers, and employees.
For companies working with complex supply chains, or that store large amounts of personal and business data, this scenario means simultaneously managing business continuity, market reputation, and relationships with regulatory authorities. In this context, a digital security strategy for SMEs is no longer optional, but a basic requirement for participating in tenders, collaborating with large groups, and responding to increasingly detailed security questionnaires.
In parallel, the European Directive NIS2 it extends and strengthens the regulatory framework on network and information system security, bringing many more companies under a perimeter of formal obligations. For businesses, this means moving from a “reactive” approach to security to a structured cybersecurity model for companies oriented toward cyber risk management.
The problem: high risk, fragile infrastructure, and stricter requirements
In many organizations, the IT infrastructure has grown incrementally: servers added over time, outdated VPNs, firewalls not always updated, backups present but untested, and weak password and access policies. In this scenario, the probability of operational freezes, data loss or encryption, and significant financial impacts in the event of an incident increases, as also shown in the focus Digital threats: protect your business .
The new regulations instead require adequate technical and organizational measures, incident management procedures, and continuous oversight of critical aspects. For many companies, this means bridging the gap between what is done today and what is required in terms of security maturity, also in light of the data protection obligations introduced by European initiatives such as the Data Act 2025 .
What NIS2 asks of companies (in practice)
From an operational point of view, NIS2 can be translated into some key requests:
- Risk governance, with defined roles and responsibilities.
- Documented information and infrastructure security policies.
- Minimum technical measures: vulnerability management, regular patching, strong authentication, data encryption, network segmentation.
- Updated and tested business continuity and disaster recovery plans.
- Monitoring of security events and incident response procedures.
- Structured training and awareness programs for staff and collaborators.
For the official framework of requirements, the NIS2 directive is described on the European Commission website in the section dedicated to the security of network and information systems. For more complex projects, these elements are often integrated with other regulatory and normative references, including the evolutions introduced by AI Act 2026 for solutions based on artificial intelligence.
A simple business case for cybersecurity
Building a business case for cybersecurity for companies means estimating the ratio between the cost of protection measures and the potential economic impact of a serious incident. Some key variables are: probability of an incident, days of downtime, average daily turnover, extraordinary recovery costs, any penalties and reputational damage.
On the cost front, infrastructures and services such as backup and business continuity, perimeter and endpoint protection, vulnerability management, training, and monitoring are typically considered. A concrete example is the adoption of solutions for Cloud backup and business continuity , which allow for the rapid restoration of data and services in the event of an incident, reducing the overall impact on the business.
A practical way to build the business case is to start with one or two realistic scenarios, for example: “what happens if I can’t issue invoices for 3 days?” or “what happens if I lose the project history of the last 5 years?”. Starting from these questions, it is possible to estimate a range of potential damage, including not only the immediate shutdown, but also the slowdown of activities in the following weeks, the time spent by management in emergency meetings, and the unplanned hours of external consultants.
Once this fork is defined, it becomes easier to compare the investment required by a three-year security plan (backup, monitoring, vulnerability assessment, training, infrastructure updates) with the cost of a single serious incident. In many cases, especially in SMEs, the cost of just one serious breach is enough to amply repay the investment needed to raise the cybersecurity level for companies, as also shown by analyses of corporate cybersecurity scenarios.
Small, medium, and large companies: same logic, different priorities
The underlying logic applies to all companies, but priorities change based on organizational size and complexity .
Small companies
Small companies often do not have a structured internal IT department and rely on an external partner for the continuous management of infrastructure, helpdesk, and critical services. In these contexts, the main objective is to build an essential but solid security foundation: email protection, strong authentication, reliable backups, and correct design of the business networking .
Medium-sized companies
In medium-sized companies, the application ecosystem is more complex (ERP, CRM, production software, hybrid environments) and requires greater integration between technical measures and processes. The formalization of policies and procedures, the introduction of centralized logs and monitoring systems, as well as periodic security posture checks, become central. In this context, activities such as Vulnerability assessment and penetration testing they help identify the most exposed areas and define concrete intervention priorities.
Large or high-criticality companies
Large companies or those operating in critical sectors (energy, transport, healthcare, finance, essential services) are more often included in the direct scope of NIS2 and other specific regulations. In these contexts, security is managed as an ongoing program, with reference frameworks, periodic audits, and particular attention to the supply chain. The design and evolution of the infrastructure – often based on data centers, virtualised environments, and cloud – requires 360-degree cybersecurity approaches for companies, such as those also adopted in projects for Cybersecurity for law firms in 2026 .
In all these dimensional bands, the role of internal IT (when present) also changes: in smaller realities, IT is often focused on solving daily problems and operations, while in medium and large ones, it is called upon to participate in defining policies, processes, and strategic technological choices. In practice, IT is no longer just "the one who fixes computers", but a function that works together with management, compliance, and other business functions to define priorities, service levels, budgets, and the security evolution roadmap.
In this step, it is often useful to have a partner who knows both the technical and regulatory aspects, capable of translating NIS2 requirements into concrete actions: which systems to update first, which logs to collect, which controls to budget for this year, and which to plan for subsequent ones.
Five "non-negotiable" controls for corporate security
Regardless of the sector, every company can start with five basic controls that form the minimum core of an effective business cybersecurity strategy.
1. Backup and business continuity
Properly designed backup systems, featuring encryption, redundancy, data immutability, and periodic recovery tests, help limit the impact of ransomware or human error. The goal is to ensure not only data copying, but the rapid recovery of critical services in emergency scenarios, thanks also to solutions such as Cloud Run BC Desk designed for cloud service continuity.
2. Strong authentication and identity management
Multi-factor authentication (MFA) for administrative accounts and privileged access users drastically reduces the risk of compromises related to credential theft or reuse. Together with robust password policies, centralized identity management, and timely revocation of access in case of departures, it becomes an essential requirement also for compliance purposes, especially to prevent scenarios of Digital Identity Theft increasingly frequent in the business environment.
3. Email, data, and hybrid work protection
Email remains one of the main attack vectors, including phishing, malicious attachments, and links to compromised sites. Advanced filtering systems, attachment analysis, protection of certified mail where used, and correct settings at the DNS and mail authentication level are key elements for reducing the risk of incidents related to digital communication, in environments often based on tools such as Microsoft 365 and hybrid work scenarios.
A typical example is the phishing campaign that simulates communication from the bank or the most used cloud service provider in the company. A single click on a malicious link can lead to the entry of credentials on a fake page and pave the way for unauthorized money movements, changes to supplier bank details, or unauthorized access to management's email.
With adequate email filtering solutions, link controls, strong authentication on critical accounts, and periodic training, the risk associated with this type of attack is significantly reduced, transforming the user from a weak link into an active part of the defense.
4. Monitoring, logging, and vulnerability management
The collection and analysis of security logs allow for the detection of anomalous behaviors and intrusion attempts, while vulnerability management serves to reduce the ‘attack surface’ through patches and correct configurations. In this context, a structured corporate network, with segmentation, next-generation firewalls, and well-defined access rules, helps to limit the spread of any compromises and integrates with cloud and on-premise solutions described in the section Modern IT technologies for companies and professionals .
5. Continuous training and incident response plans
People remain a crucial element of the security posture: seemingly minor errors can pave the way for complex attacks. Recurring training and awareness programs, accompanied by practical examples and simulations , and documented and tested incident response plans at least once a year, are required by both best practices and regulatory standards.
An often underestimated element is the periodic testing of incident response plans: simulating an attack scenario, even just once a year, allows for verification of reaction times, clarity of roles, and quality of available information. In many cases, these exercises reveal simple areas for improvement (e.g., outdated contact lists, hard-to-find documents, unmapped critical dependencies) that can be corrected before finding yourself in a real emergency situation.
Lanpartners' role: from risk to security roadmap
Lanpartners is an IT company based in Milan, specialized in solutions for businesses and professionals and operating throughout the Italian territory. With strong expertise in infrastructure, cybersecurity for businesses, cloud and technological innovation projects, Lanpartners boasts a particular specialization in the law firm sector, where the protection of sensitive data and regulatory compliance are fundamental requirements. Through the IT Concierge® model, we integrate managed services, operational support, and strategic consulting to help organizations design and maintain a secure IT ecosystem aligned with regulatory requirements over time.
In daily practice, this translates into projects that almost always start from a snapshot of the current state: inventory of systems, network analysis, verification of cloud backup solutions, evaluation of credentials and permissions, check of the posture of devices used in the company and in smart working. Based on what emerges from this analysis, a prioritized plan is built, distinguishing what needs to be fixed immediately (e.g., an exposed server or non-functional backups) from what can be scheduled for the following months.
For organizations that have already started modernization projects, such as migrating to Microsoft 365 or hybrid cloud environments, Lanpartners helps you get the most out of the security features already built into your platforms, integrating them with networking, monitoring and end-to-end business cybersecurity solutions designed for complex professional environments.
In a path towards NIS2 compliance and greater digital resilience, support can include analysis of the current state, roadmap definition, implementation of priority technical and organizational measures, verification activities, and training programs for staff. Companies wishing to learn more can contact Lanpartners directly through our page Contacts to assess their situation and define a concrete action plan.
Frequently asked questions
What does the NIS2 directive require of companies in practical cybersecurity terms?
NIS2 requires technical and organizational measures appropriate to the risk. In practice, this means governance with defined roles, documented security policies, vulnerability management and patching, strong authentication, encryption, network segmentation, tested business continuity and disaster recovery plans, event monitoring, incident response, and staff training.
What are the minimum cybersecurity controls that every company should adopt?
Every company can start with five basic controls: encrypted and immutable backups with periodic restoration tests, multi-factor authentication (MFA), advanced email protection, log monitoring with vulnerability management, and continuous training with incident response plans documented and tested at least once a year.
How is the return on investment in cybersecurity calculated for an SME?
Compare the cost of protection measures with the economic impact of a serious incident. Start with one or two realistic scenarios, for example, three days without being able to issue invoices, estimating downtime, daily turnover, restoration costs, penalties, and reputational damage. Often, a single serious breach exceeds the cost of a three-year plan.
How do cybersecurity priorities change between small, medium, and large companies?
Small businesses focus on an essential foundation: email protection, strong authentication, reliable backups, and a well-designed network. Medium-sized ones formalize policies, introduce centralized logs, monitoring, vulnerability assessments, and penetration tests. Large or high-criticality organizations manage security as a continuous program, with frameworks, periodic audits, and attention to the supply chain.
Why is multi-factor authentication (MFA) important for compliance and corporate security?
MFA drastically reduces the risk of compromises due to theft or reuse of credentials, especially on administrative accounts and users with privileged access. Together with robust passwords, centralized identity management, and timely revocation of access when a person leaves the company, it is an essential requirement for NIS2 compliance as well.
How can an IT partner help a company prepare for NIS2 compliance?
An IT partner starts with a snapshot of the current state: system inventory, network analysis, backup verification, and checking credentials and permissions. Then, it builds a priority-based plan, distinguishing urgent interventions from programmable ones, and supports the implementation of measures, verifications, and staff training. Lanpartners operates this way with the IT Concierge® model.
